Sentinel Agentic SOC: AI-Assisted Detection, Investigation & Response
Security teams drown in disconnected alerts across firewalls, endpoints, cloud directories, and email gateways. Sentinel Agentic SOC unifies your multi-vendor security stack into a single 4-stage operational flywheel—Detect, Investigate, Respond, and Hunt—powered by specialized AI investigation agents and governed by human-in-the-loop containment controls.
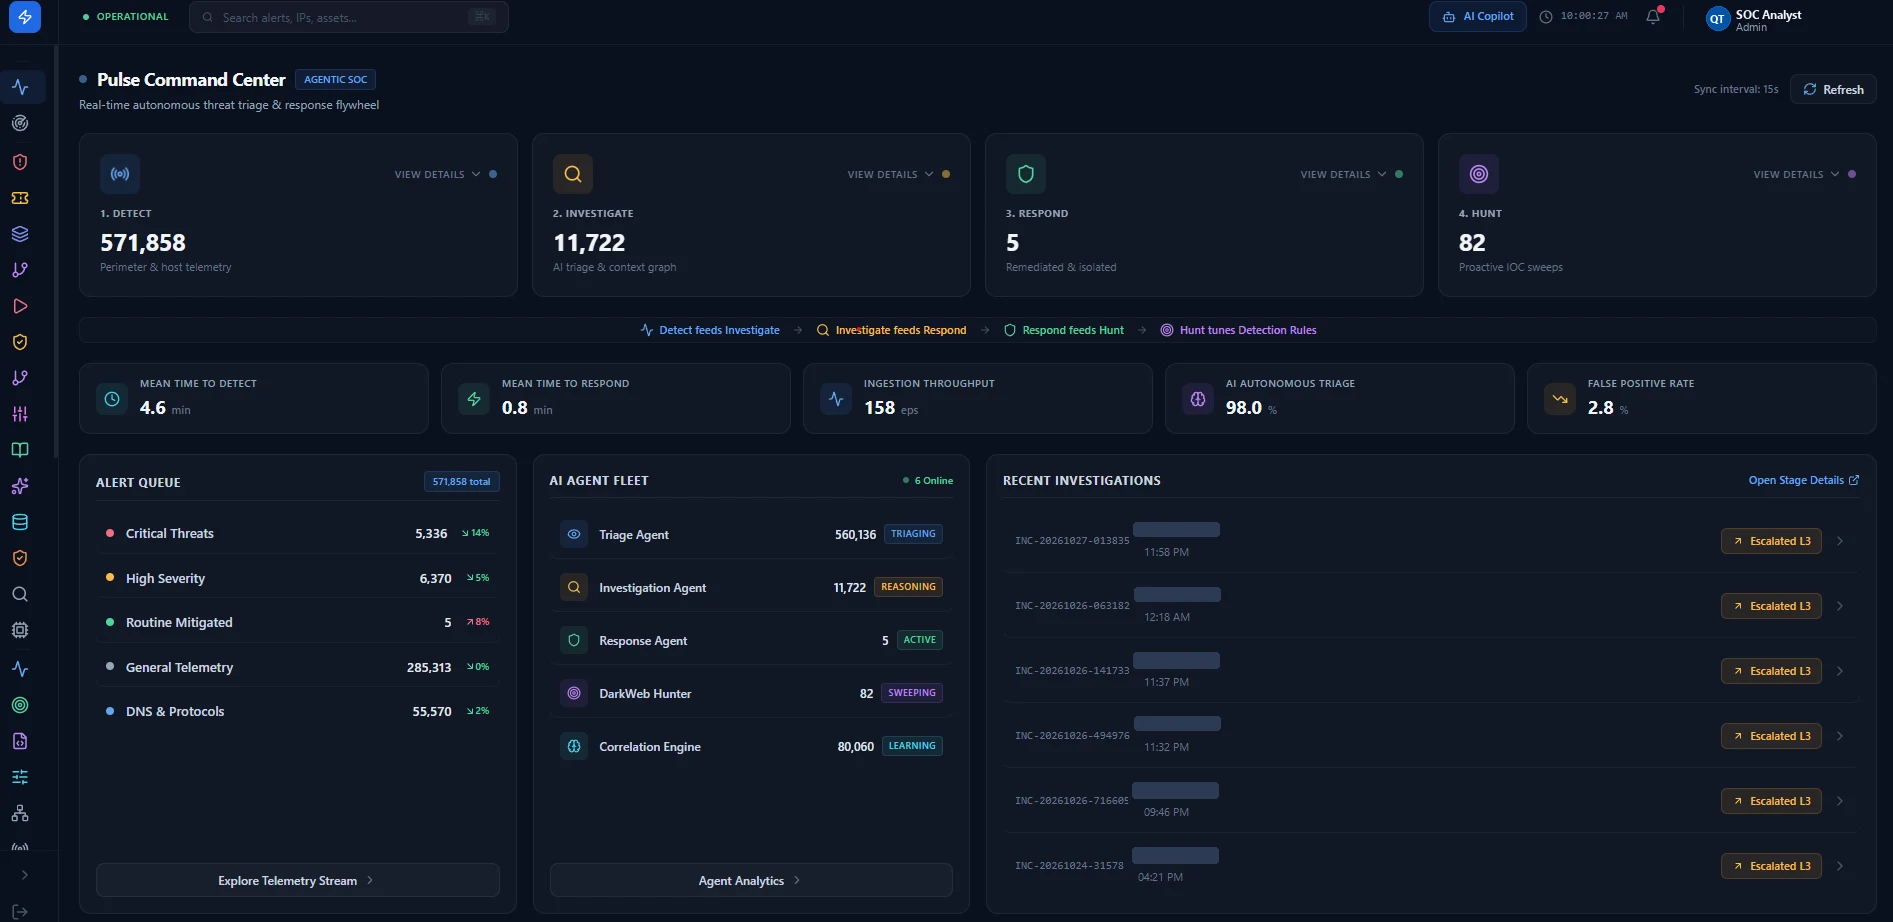
Actual platform screenshot: QueryTel Sentinel v5.0 Pulse Command Center (sanitized for web display).
Specialized AI Agents for Triage & Investigation. Human Approval Gates for Containment.
In Sentinel Agentic SOC, AI agents handle the repetitive heavy lifting of normalizing hundreds of thousands of telemetry logs, grouping related behaviors, and assembling cross-vendor attack narratives—while human analysts retain authority over infrastructure-altering actions.
1. Triage Agent
Ingests normalized events across firewalls, endpoints, and identity sensors, clusters repetitive scanner noise, and separates routine baseline traffic from high-priority escalations.
2. Investigation Agent
Enriches escalated alerts with environmental asset context, user identity risk history, and custom AI investigation skills to produce structured root-cause summaries.
3. Correlation Engine
Links events across 5 security pillars—ThreatGate MXDR, Entra ID, Purview, Defender/ThreatDown EDR, and FortiGate—into chronological MITRE ATT&CK kill-chain stories.
4. Response Agent
Prepares concrete containment steps—including FortiOS CLI address-group block scripts, session revocations, and Zoho Desk incident tickets—ready for analyst execution or approval.
5. DarkWeb Hunter
Sweeps external threat reports (CISA KEV, Abuse.ch Feodo) and dark web credential exposure feeds against internal telemetry and domain assets.
6. QueryTel Copilot & Workflow Assistant
Interactive AI assistant drawer (Llama 3.2 engine) that answers analyst queries over live FortiGate and FortiAnalyzer log streams and assists in designing SOAR workflows.

Explore Sentinel Agentic SOC Across 8 Core Operational Views
Every screenshot below is captured directly from QueryTel Sentinel v5.0 and sanitized to protect operational identifiers. Select any module tab or click an image to expand.
Multi-Vendor Attack Story & MITRE Correlation
Instead of forcing analysts to pivot between five separate consoles, Sentinel automatically chains related detections across ThreatGate MXDR, Microsoft Entra ID, Microsoft Purview, Defender / ThreatDown EDR, and FortiGate Firewalls into a single chronological incident story mapped to MITRE ATT&CK techniques.
- Sequential 5-step Cyber Kill-Chain visualization
- Per-stage forensic telemetry inspection
- Plain-language incident summary narrative


Built for Multi-Vendor Enterprise Security Stacks
Sentinel Agentic SOC connects directly to the security infrastructure Canadian enterprises rely on—normalizing syslog streams, REST APIs, and audit ledgers into one operational schema:
Deploy as Software or Managed Service
Empower your in-house security analysts with the Sentinel Agentic SOC platform, or pair it with QueryTel's Canadian 24/7 Managed SOC & MXDR operations team.
Sentinel Agentic SOC — Architecture & Governance FAQs
If/Else, Switch, and For Each loops), an embedded AI Workflow Assistant, version control, and pre-built playbook templates.
.pdf), Excel (.xlsx), and CSV.
Experience Sentinel Agentic SOC v5.0
Book a live technical session with QueryTel's security architects to explore multi-agent alert triage, MITRE ATT&CK kill-chain correlation, and human-gated SOAR workflows.