QueryTel Email MXDR: Advanced Email Threat Detection & Identity Correlation
Traditional email gateways stop looking once an email reaches the inbox. QueryTel Email MXDR (powered by ThreatGate MXDR v1.1) combines inbound email threat scoring with Microsoft Entra ID sign-in telemetry, Microsoft Purview mailbox audit trails, and Microsoft Defender XDR to expose phishing lures, Business Email Compromise (BEC), and unauthorized inbox forwarding rules across the full attack lifecycle.

Actual platform screenshot: ThreatGate MXDR v1.1 console integrated inside QueryTel Sentinel (sanitized for web display).
From Spearphishing Lure to Mailbox Persistence: One Correlated Story
Enterprise email security platforms such as Proofpoint established the importance of defending the corporate inbox, but modern Business Email Compromise rarely stops at a single email event. QueryTel Email MXDR correlates email detections with downstream identity, compliance, endpoint, and perimeter firewall signals to trace the complete MITRE ATT&CK sequence.
Initial Access
Detects spearphishing links and credential-harvesting lures via ThreatGate MXDR and correlates post-delivery malicious URL removal via Microsoft Defender XDR.
Credential Access
Flags geographic velocity anomalies (e.g., >900 km/h Impossible Travel sign-ins) and risky user state transitions in Microsoft Entra ID.
Mailbox Persistence
Audits Exchange Online for unauthorized New-InboxRule auto-forwarding rules and Add-MailboxPermission delegation.
Exfiltration Monitoring
Tracks sensitive SharePoint/OneDrive file downloads, external anonymous sharing links, and Purview DLP policy blocks on regulated data.
Human-Gated Response
Correlates outbound C2 blocks on FortiGate firewalls and stages human-approved remediation steps (rule revocation & FIDO2 re-authentication).

Inside the QueryTel Email MXDR & Microsoft 365 Defense Suite
Every capability below is verified directly against the implemented ThreatGate MXDR v1.1 and QueryTel Sentinel v5.0 modules. Click any dashboard view to inspect the interface at full resolution.
Inbox Auto-Forwarding Rule & Mailbox Delegation Auditing
When attackers compromise an executive or finance mailbox, they frequently create silent inbox rules to forward emails containing payment instructions to external addresses. QueryTel Email MXDR ingests the Microsoft Purview Unified Audit Log (UAL) across 6 Microsoft 365 workloads with 180-day forensic retention:
-
Suspicious Auto-Forwarding Detection: Flags
New-InboxRuleevents redirecting emails with keywords like invoice, wire, or payment. -
Privilege & Mailbox Delegation: Tracks
Add-MailboxPermissionevents granting Send-As or Read rights on executive mailboxes. -
DLP & SharePoint Governance: Logs Purview DLP policy blocks (
DLPPolicyMatch), confidential file downloads, and anonymous sharing invitations with CSV audit export.

Entra ID Impossible Travel & Risky Identity Correlation
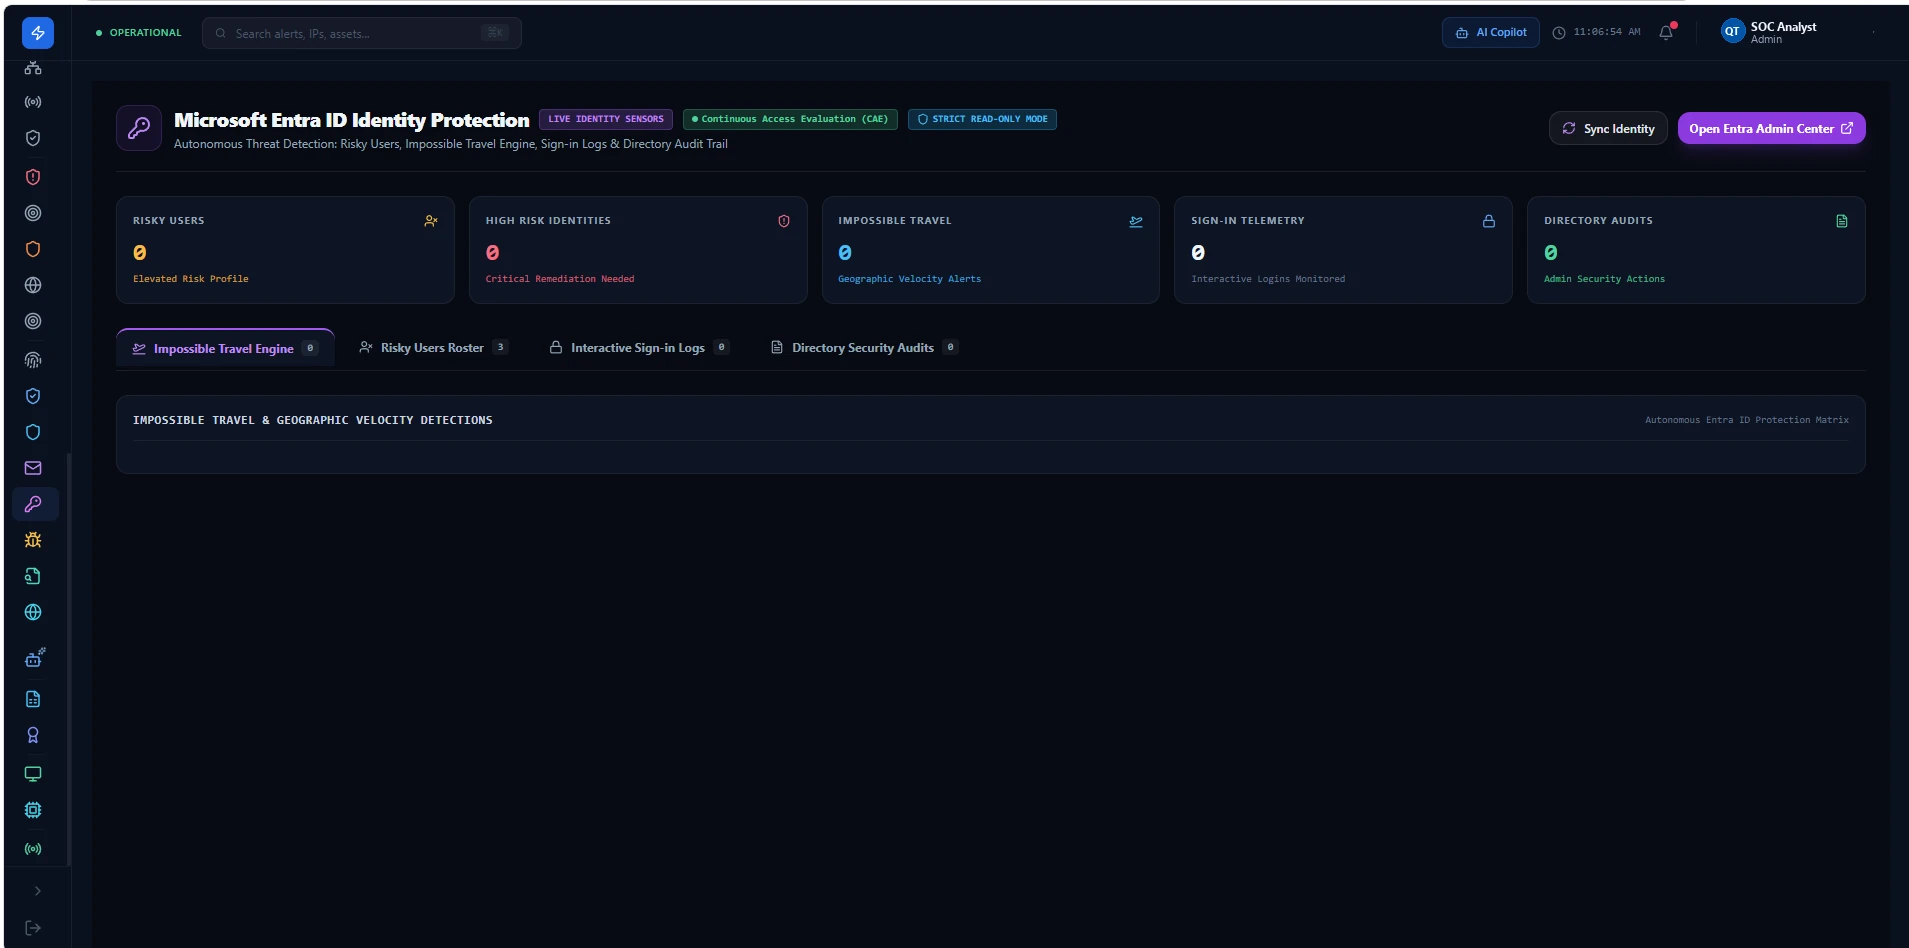
Phishing attacks succeed when stolen credentials or session tokens are used to authenticate from unauthorized locations. QueryTel correlates email activity with live Microsoft Entra ID Identity Protection sensors:
- Impossible Travel Engine: Detects geographic velocity anomalies between consecutive sign-ins alongside interactive login monitoring.
- Continuous Access Evaluation (CAE): Monitors risky user rosters, high-risk identity states, and administrative directory security audits.
- Strict Read-Only Ingestion: Connects using read-only sensor permissions so monitoring never disrupts production identity workflows without administrator approval.
Post-Delivery Malicious URL Removal & Endpoint Alert Alignment
Delayed weaponization is a common evasion tactic where links become malicious only after an email lands in the user's inbox. Through native Microsoft Defender XDR correlation, QueryTel tracks post-delivery email alerts alongside endpoint detections:
-
Post-Delivery URL & Message Removal: Surfaces
T1566.002alerts when messages containing malicious URLs are removed after delivery or reported by users as junk. - AI Anomalous Email Parser Skill: Leverages Sentinel's built-in AI Skill Library and QueryTel Copilot to assist analysts in inspecting headers, sender reputation, and correlated host activity.

Read-Only Telemetry Ingestion & Human-Approved Containment
Security tools should never lock out legitimate executives or disrupt critical business workflows without oversight. QueryTel Email MXDR is engineered around transparent operational guardrails:
Strict Read-Only Sensor Mode
Microsoft Entra ID and Defender XDR connectors operate in Strict Read-Only Mode during telemetry ingestion, ensuring continuous visibility without unapproved write mutations to your directory.
Human-in-the-Loop Directives
Containment steps—such as revoking external inbox forwarding rules, isolating a host, or enforcing FIDO2 re-authentication—are presented as prioritized action items for administrator confirmation.
Part of the 5-Pillar Sentinel Architecture
QueryTel Email MXDR works seamlessly alongside Sentinel Agentic SOC or can be paired with QueryTel's 24/7 Managed SOC & MXDR cybersecurity team.
QueryTel Email MXDR — Technical FAQs
T1566.002), geographic velocity anomalies via the Impossible Travel Engine (T1078.004), and unauthorized Exchange Online inbox auto-forwarding rules targeting financial keywords such as invoice, wire, or payment (T1114.003).
See QueryTel Email MXDR in Action
Schedule a live technical walkthrough of ThreatGate MXDR v1.1, Entra ID Impossible Travel correlation, and Purview BEC inbox rule auditing with QueryTel's security engineering team.