Amazon Web Services • ca-central-1 (Montreal) & ca-west-1 (Calgary)

Enterprise AWS Cloud Architecture, Migration & 24/7 Managed Ops.

QueryTel designs, migrates, secures, and operates mission-critical Amazon Web Services environments across Canada. From multi-account AWS Control Tower Landing Zones and Amazon EKS Kubernetes to Direct Connect SD-WAN, FinOps cost reduction, and live threat correlation with QueryTel Sentinel Agentic SOC.

99.99%
Multi-AZ High Availability
35%+
Avg. FinOps Cloud Savings
100%
Canadian Data Residency
24/7
Sentinel SOC + NOC Ops
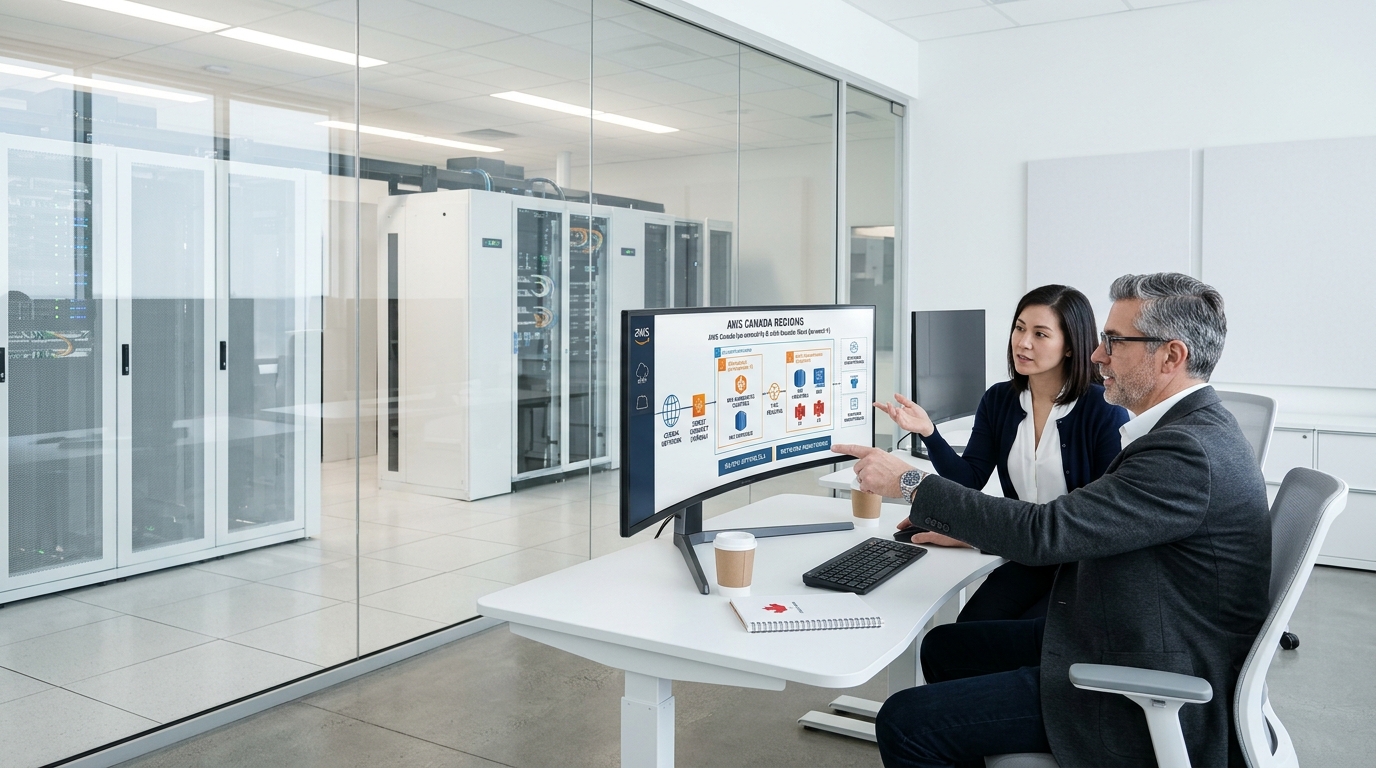
QueryTel Canadian AWS Cloud Engineering & Architecture Command Center
REGION: ca-central-1 • ca-west-1 HEALTHY

Sovereign Multi-Account AWS Control Tower & Direct Connect Fabric

Engineered Across the AWS Stack:
AWS Control Tower Amazon EC2 & Graviton4 Amazon EKS & ECS Fargate Amazon RDS & Aurora Amazon S3 Object Lock AWS Direct Connect IAM Identity Center GuardDuty + Sentinel SOC
Why Enterprises Re-Architect AWS With QueryTel

Stop Paying for Unmanaged Cloud Sprawl & Security Blind Spots

Many organizations lift-and-shift workloads into a single flat AWS account—leading to runaway NAT Gateway and EC2 bills, over-privileged IAM keys, and unmonitored CloudTrail logs. We replace ad-hoc cloud setups with deterministic Well-Architected infrastructure.

Common Unmanaged AWS Risks

Flat Single-Account Sprawl & Runaway Spend

  • Single-Account Blast Radius: Production, staging, and developer workloads mixed in one VPC without AWS Organizations or Service Control Policies (SCPs).
  • Long-Lived Static IAM Access Keys: Developers sharing permanent `AKIA...` access keys in `.env` files instead of short-lived federated STS tokens.
  • 30%–45% Wasted Monthly Spend: Oversized on-demand EC2 instances, unattached EBS volumes, and expensive cross-AZ data transfer fees.
  • Unmonitored GuardDuty & CloudTrail Alerts: Security findings sit unread in the AWS console with no 24/7 SOC correlation or automated containment.
QueryTel Well-Architected Standard

Sovereign Multi-Account AWS + 24/7 Sentinel SOC

  • Multi-Account Control Tower Landing Zones: Dedicated Security, Log Archive, Shared Network, Production, and Sandbox accounts locked to `ca-central-1` & `ca-west-1`.
  • Zero-Trust Federated SSO: Microsoft Entra ID / Okta federated into AWS IAM Identity Center with ephemeral STS session tokens and hardware MFA.
  • Continuous FinOps Cost Governance: Graviton4 modernization, Compute Savings Plans, VPC Endpoints for S3/DynamoDB, and automated right-sizing.
  • Closed-Loop Sentinel Agentic SOC Defense: Real-time GuardDuty, Security Hub, and FortiGate VM telemetry correlated with sub-second SOAR isolation.
Full-Lifecycle AWS Engineering

Six Core AWS Cloud Capabilities Engineered for Canadian Enterprises

Hover over each capability module below. Every AWS environment we deploy is codified in Terraform or AWS CloudFormation, documented with runbooks, and backed by 24/7 Canadian engineering support.

Pillar 01 • Sovereign Foundation

Canadian AWS Landing Zones & Control Tower

Multi-account AWS Organizations architecture built with AWS Control Tower, Terraform modules, and preventive Service Control Policies (SCPs) enforcing strict data residency in Montreal (`ca-central-1`) and Calgary (`ca-west-1`).

Control Tower SCP Guardrails PIPEDA / Law 25
Pillar 02 • Compute & Containers

Amazon EKS, ECS Fargate & Serverless Modernization

Refactor monolithic applications into auto-scaling microservices on Amazon EKS (Kubernetes), serverless containers on AWS Fargate, and event-driven APIs using AWS Lambda, API Gateway, and Step Functions.

Amazon EKS ECS Fargate AWS Graviton4
Pillar 03 • Data & Storage

Amazon RDS, Aurora, S3 Data Lakes & Immutable Backup

High-throughput database engineering across Amazon Aurora PostgreSQL/MySQL, RDS Multi-AZ, and DynamoDB, paired with ransomware-proof Amazon S3 Object Lock (WORM) and cross-region AWS Backup vaults.

Aurora Multi-AZ S3 Object Lock DMS Zero-Downtime
Pillar 04 • Hybrid Networking

AWS Direct Connect, Transit Gateway & Fortinet SD-WAN

Bridge Canadian offices, warehouses, and colocation racks into AWS using redundant AWS Direct Connect circuits, centralized AWS Transit Gateways, and Fortinet FortiGate-VM inspection VPCs.

Direct Connect Transit Gateway FortiGate-VM NGFW
Pillar 05 • Autonomous Cloud SecOps

AWS GuardDuty, IAM Identity Center & Sentinel SOC

Harden AWS with IAM Identity Center, AWS WAF, Shield Advanced, KMS, and GuardDuty—streaming every CloudTrail and VPC flow event into QueryTel Sentinel Agentic SOC for 24/7 autonomous containment.

GuardDuty + WAF IAM Identity Center Sentinel SOC v5.0
Pillar 06 • Cloud Economics

AWS FinOps Cost Optimization & 24/7 Managed Cloud Ops

Continuous right-sizing, Compute Savings Plans & Reserved Instance portfolio management, S3 lifecycle tiering, automated OS patching via AWS Systems Manager, and 24/7 incident response.

Savings Plans Systems Manager 35%+ Cost Reduction
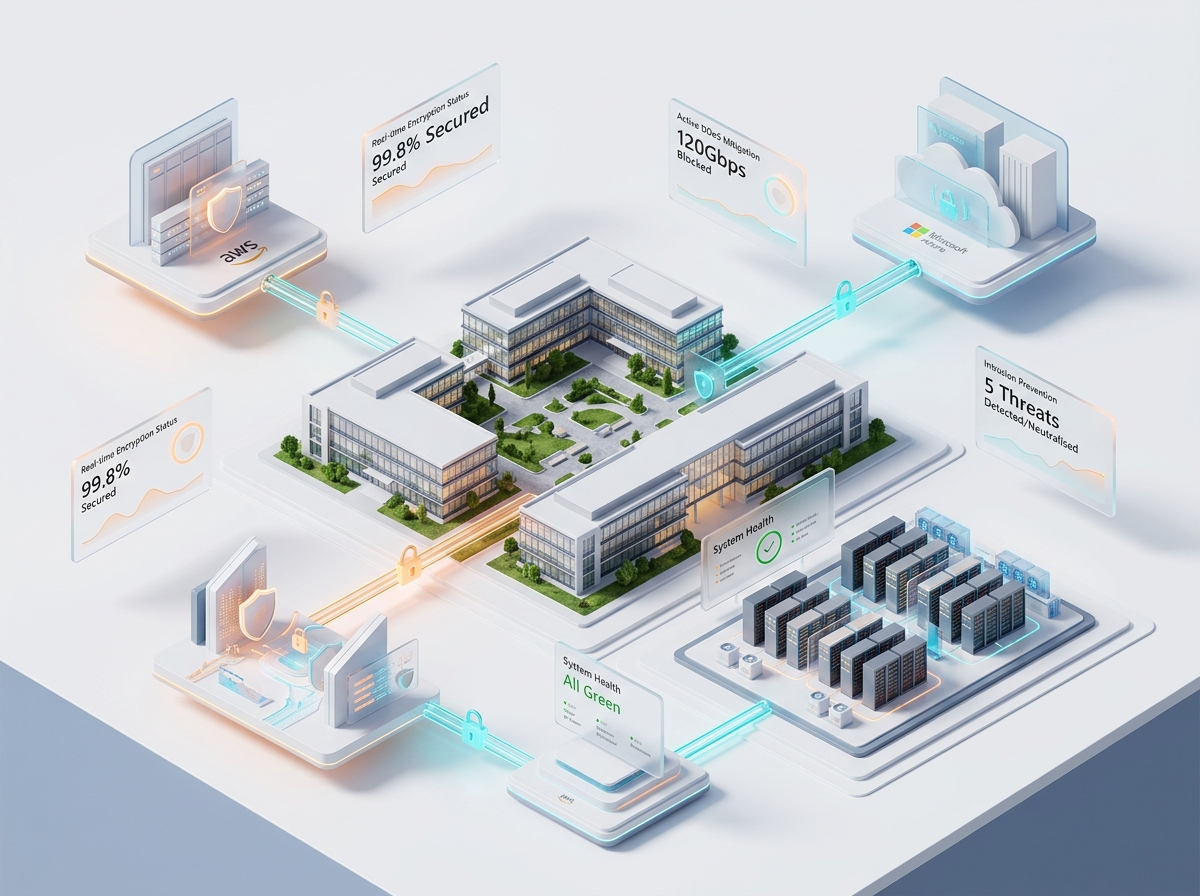
3D HYBRID AWS TOPOLOGY • CANADA 120Gbps DDoS Protected
3D Isometric AWS and Hybrid Cloud Topology with Real-Time Encryption and DDoS Protection
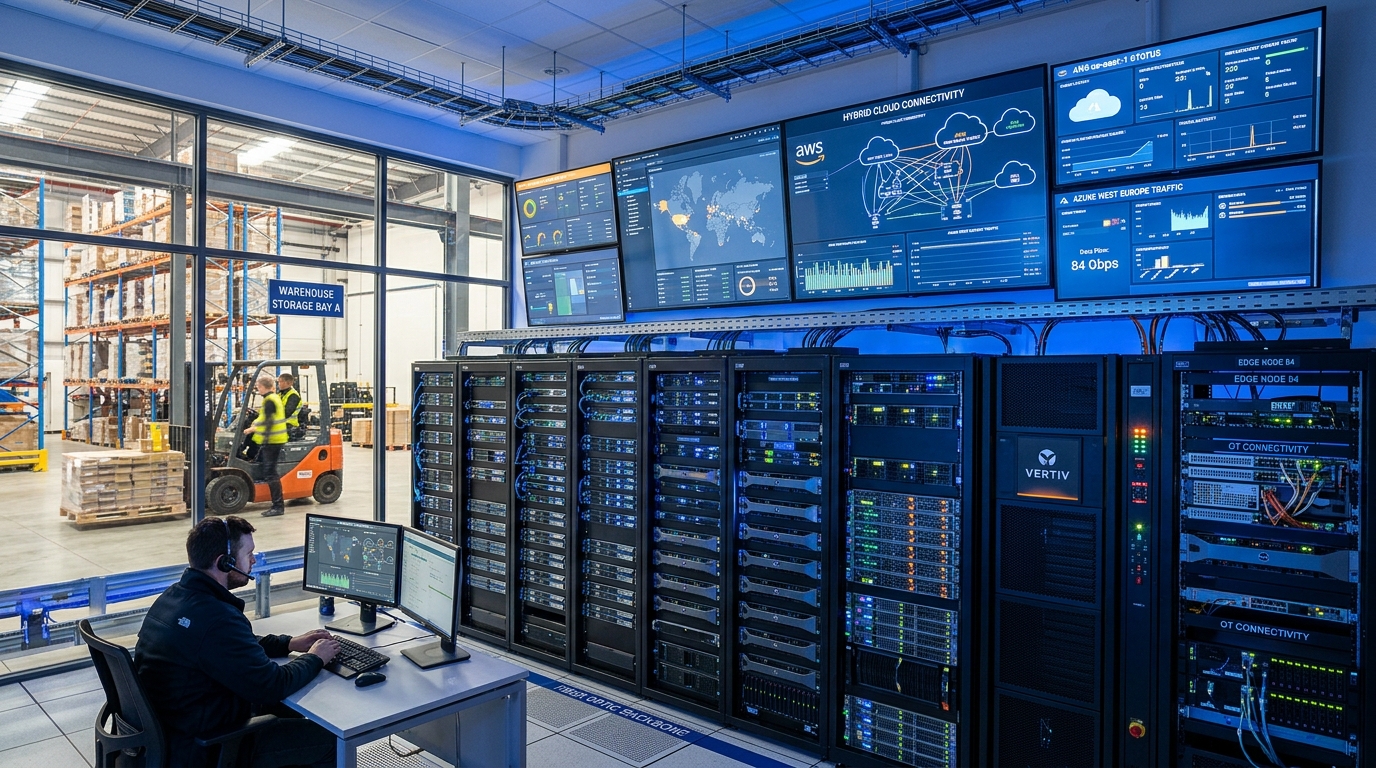
QueryTel Hybrid AWS Cloud Connectivity Operations Center
Hybrid Edge-to-AWS Operations
Direct Connect + Warehouse OT/IT Integration
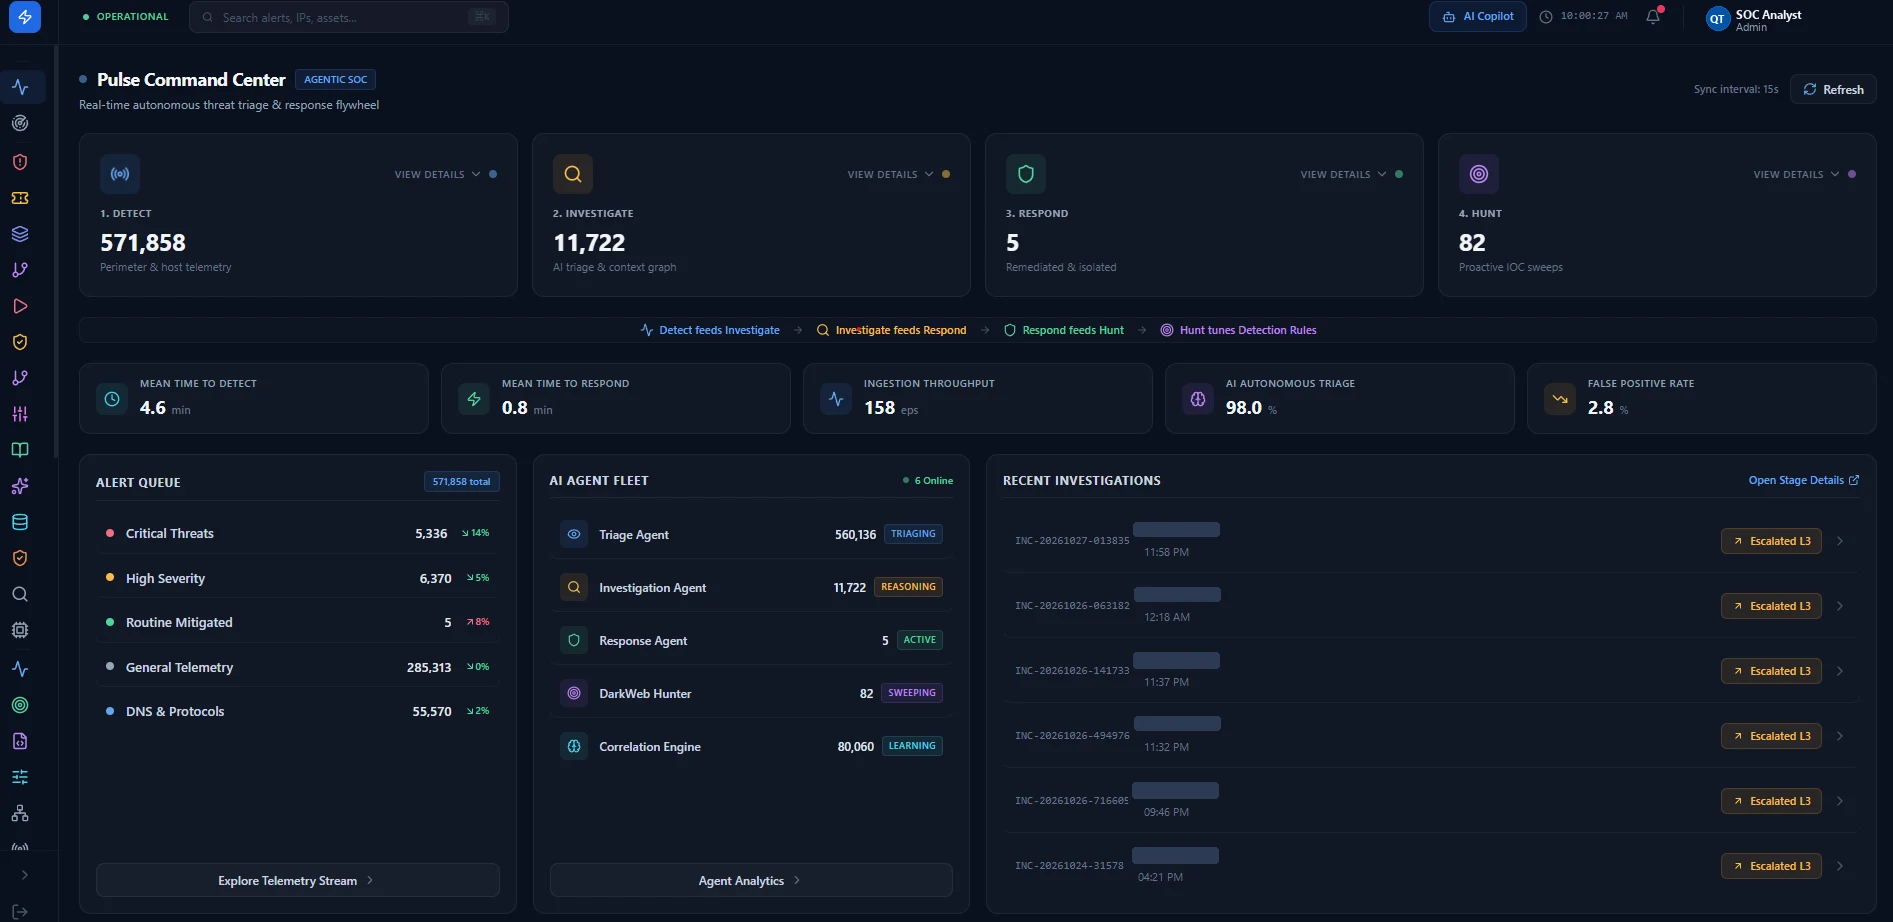
QueryTel Sentinel Agentic SOC v5.0 Monitoring AWS Telemetry
Sentinel Agentic SOC v5.0
Live GuardDuty, CloudTrail & FortiGate Correlation
Unified Cloud Engineering + Proprietary SecOps

Every AWS Account Protected by QueryTel Sentinel Agentic SOC

Unlike generic cloud consultancies that hand over an AWS account and walk away, QueryTel wires your AWS control plane directly into our proprietary Sentinel Agentic SOC (v5.0) platform and 24/7 Canadian NOC/SOC command center.

01

Real-Time CloudTrail & GuardDuty Ingestion

Detects unauthorized IAM privilege escalation, anomalous S3 bucket policy changes, EC2 crypto-mining behavior, and compromised STS session tokens within seconds.

02

Cross-Domain Kill-Chain Correlation

Correlates AWS VPC flow anomalies with QueryTel Email MXDR phishing alerts, Microsoft Entra ID sign-in risks, and Fortinet FortiGate SD-WAN firewall logs.

03

Automated SOAR Containment & CSPM

Executes human-approved or autonomous playbooks to quarantine compromised EC2 instances via Security Group isolation, revoke IAM sessions, and block malicious IPs at AWS WAF.

AWS Migration Acceleration Methodology

Zero-Disruption AWS Migration in Four Deterministic Phases

Structured engineering execution from initial Total Cost of Ownership (TCO) assessment to 24/7 managed cloud operations.

PHASE 01 • WEEKS 1–2

Assess & FinOps TCO Audit

Automated dependency discovery across on-premises VMware/Hyper-V or legacy cloud accounts, AWS Well-Architected Pillar scoring, and 3-year FinOps Savings Plan modeling.

PHASE 02 • WEEKS 3–4

Mobilize & Landing Zone IaC

Deploy multi-account AWS Control Tower in `ca-central-1` / `ca-west-1`, configure Entra ID SAML SSO to IAM Identity Center, and establish Fortinet SD-WAN / Direct Connect links.

PHASE 03 • WEEKS 5–8

Migrate & Modernize

Execute block-level replication via AWS MGN, continuous database sync via AWS DMS, and containerization onto Amazon EKS / ECS Fargate with verified cutover windows.

PHASE 04 • ONGOING 24/7

Operate, Secure & Optimize

24/7 Sentinel Agentic SOC monitoring, automated AWS Systems Manager patching, immutable S3 backup verification, and monthly FinOps cost-optimization reviews.

AWS Technical & Compliance FAQs

Frequently Asked Questions About QueryTel AWS Services

QueryTel provisions multi-account AWS Landing Zones using AWS Control Tower and Service Control Policies (SCPs) that cryptographically restrict resource creation to Canadian AWS Regions—specifically ca-central-1 (Montreal) and ca-west-1 (Calgary). We also enforce customer-managed AWS KMS encryption keys and S3 bucket residency guardrails to satisfy PIPEDA, Quebec Law 25, PHIPA, and SOC 2 Type II requirements.
QueryTel integrates your AWS accounts directly with our proprietary Sentinel Agentic SOC v5.0 platform. We ingest AWS CloudTrail management and data events, Amazon GuardDuty findings, AWS Security Hub posture alerts, VPC Flow Logs, and FortiGate VM perimeter telemetry into Sentinel's 5-engine correlation fabric—enabling automated MITRE ATT&CK kill-chain mapping and sub-second SOAR containment.
Yes. Through our AWS FinOps practice, QueryTel routinely reduces monthly AWS cloud expenditure by 28% to 42%. We eliminate orphaned EBS volumes and idle NAT Gateways, transition workloads to AWS Graviton4 processors, architect S3 Intelligent-Tiering lifecycle policies, and manage Compute Savings Plans and RDS Reserved Instances.
Absolutely. QueryTel engineers resilient hybrid cloud topologies combining AWS Direct Connect, AWS Transit Gateway, and Fortinet FortiGate VM Next-Generation Firewalls. This links your corporate headquarters, manufacturing plants, and distribution warehouses directly to private AWS subnets with deterministic sub-10ms latency and end-to-end IPsec/MACsec encryption.
Yes. Using the AWS Migration Acceleration methodology, AWS Application Migration Service (MGN) block-level replication, and AWS Database Migration Service (DMS) with continuous Change Data Capture (CDC), we execute cutovers during scheduled maintenance windows with near-zero downtime and validated rollback runbooks.
Yes. QueryTel configures SAML 2.0 and SCIM automatic provisioning between Microsoft Entra ID and AWS IAM Identity Center. This eliminates static IAM access keys, enforces hardware FIDO2 MFA and Conditional Access policies before an engineer can assume an AWS IAM Role, and logs every session into QueryTel Sentinel SOC.
Schedule Your AWS Architecture & FinOps Assessment

Ready to Modernize, Secure & Optimize Your AWS Cloud?

Speak directly with QueryTel's Senior AWS Cloud & Security Architects. We will review your VPC topology, IAM posture, Canadian compliance requirements, and FinOps cost-saving opportunities.