Air-gap corporate email and office workstations from critical warehouse management systems (WMS), ammonia refrigeration chillers, conveyors, and SCADA PLCs using managed FortiGate firewalls.
Why Flat Networks Threaten Canadian Industrial Infrastructure
Warehouses, cross-dock facilities, cold storage distribution hubs, and food processing plants have rapidly digitized. However, connecting corporate office networks directly to factory floor controls creates an open highway for catastrophic lateral ransomware attacks.
Comprehensive IT/OT Cybersecurity Engineered by QueryTel
We bridge the historical divide between corporate IT compliance and operational technology uptime requirements, delivering defense-in-depth without slowing down production lines.
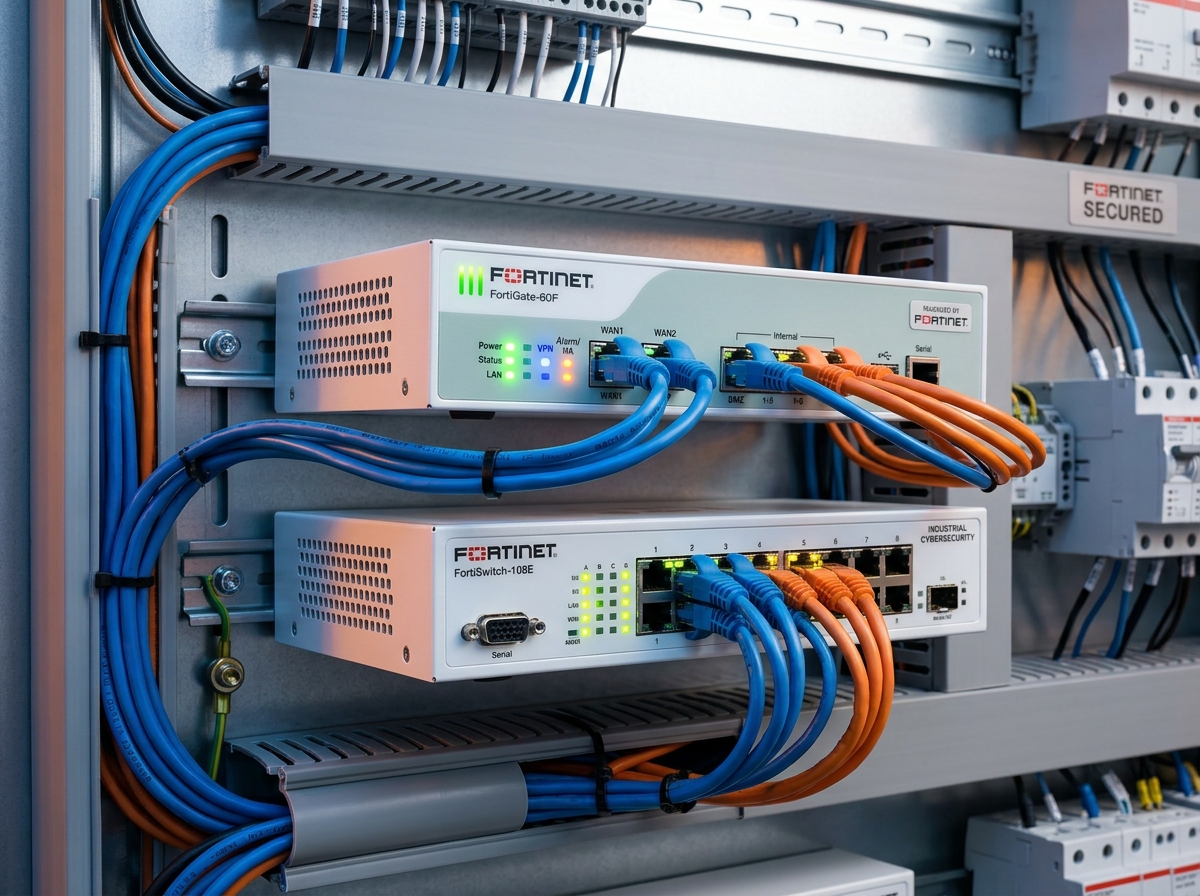
Deployment of Fortinet appliances engineered specifically for harsh industrial and distribution environments. We deploy high-throughput enterprise appliances (FortiGate 60F, 70F, 100F, and 200F series) for central distribution control rooms, alongside DIN-rail mounted ruggedized units (FortiGate Rugged 60F / 70G) built to withstand sub-zero cold storage freezers (-40°C), vibration, electromagnetic interference, and dust.
We architect rigorous logical separation aligned with international ISA/IEC 62443 benchmarks. We isolate Enterprise IT (Levels 4–5: ERP, Office 365, Billing) from Site Operations (Level 3: WMS master servers, historians) by inserting a secure Industrial Demilitarized Zone (Level 3.5 IDMZ). Critical shop-floor control systems (Level 2: HMIs, SCADA), direct machine control (Level 1: PLCs, RTUs), and physical field sensors (Level 0) operate inside micro-segmented defensive cells.
Operational technology speaks specialized industrial languages that standard firewalls cannot understand. QueryTel configures Fortinet's FortiGuard Industrial Security Service to inspect Layer 7 payloads for protocols including Modbus TCP, EtherNet/IP (CIP), PROFINET, OPC UA, BACnet IP, and DNP3. We enforce strict function-code filtering—authorizing routine operational data polling while blocking dangerous firmware re-flashes or ladder logic modifications.
Third-party support vendors (HVAC technicians, ammonia refrigeration engineers, robotic conveyor specialists, automated guided vehicle/AGV vendors) represent the #1 attack vector into industrial facilities. QueryTel replaces broad VPN connections and unmanaged remote desktop tools with encrypted FortiClient ZTNA tunnels and hardened bastion jump hosts situated inside the IDMZ.
In refrigerated logistics and cold storage warehousing, an uncontained cyber breach or unauthorized setpoint modification can cause catastrophic ammonia gas releases, regulatory fines, and millions in spoiled food or biologics. QueryTel isolates refrigeration compressor controllers, defrost cycles, temperature sensors, and emergency ventilation relays inside dedicated, cryptographically segregated VLANs with hardware bypass protection.
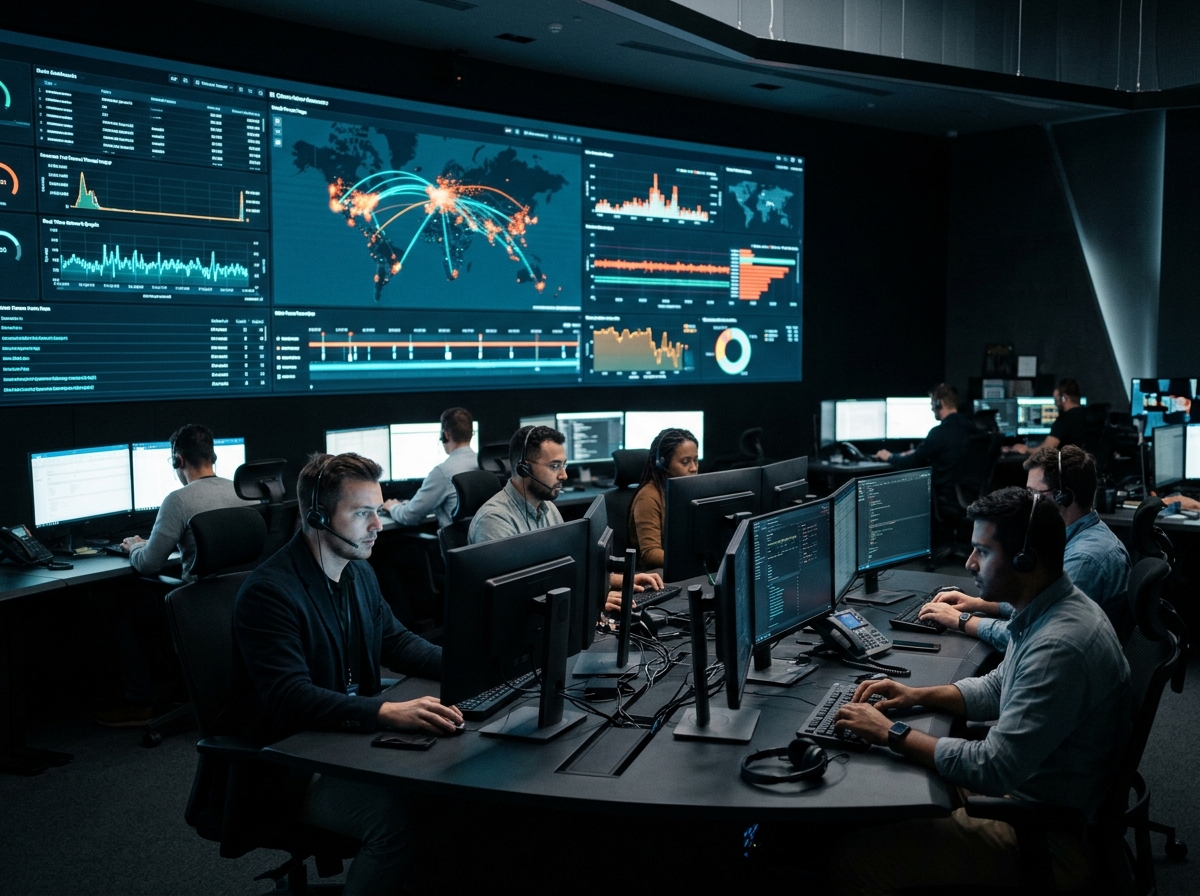
Network segregation firewalls are only as powerful as the analysts monitoring them. All Fortinet OT telemetry, syslog traffic, and firewall alarms feed directly into QueryTel's 24/7/365 Canadian Security Operations Center in Mississauga. Our SOC analysts proactively monitor for abnormal broadcast storms, unauthenticated PLC polling, brute-force attempts on jump hosts, and cross-zone policy violations.
How We Segment IT and OT Networks Without Halting Production
Industrial plant managers fear cybersecurity projects because ill-timed changes cause assembly lines or refrigeration loops to trip. QueryTel guarantees zero operational downtime through our battle-tested 4-phase rollout framework.
We tap your network switches using passive SPAN/mirror ports. We catalog every connected PLC, HMI, WMS terminal, barcode scanner, and sensor without transmitting a single active packet or disrupting control communications.
Our cybersecurity engineers design the target Purdue Model segmentation blueprint. We define VLAN allocations, Industrial DMZ boundaries, and strict firewall access control lists (ACLs) tailored to your operational workflows.
Fortinet FortiGate appliances are installed in "Monitor-Only" audit mode. We validate real-world production traffic against our proposed security policies over a 14-day cycle to ensure zero legitimate industrial packets are blocked.
We execute the cutover, activating line-rate Layer 7 Deep Packet Inspection, ZTNA remote vendor jump boxes, and real-time event streaming to our Canadian SOC for continuous threat hunting and lifecycle firmware maintenance.
QueryTel operates from our corporate headquarters at Exchange Tower, 130 King Street West, Suite 1900, Toronto, Ontario M5X 1E3. We maintain dedicated hardware pre-configuration labs where Fortinet firewalls are unboxed, updated, cryptographically provisioned, and stress-tested before deployment.
Through our nationwide field service network, we dispatch certified smart hands to industrial plants, cold storage facilities, and multi-tenant distribution parks across the Greater Toronto Area, Southern Ontario corridor, Montreal, Calgary, Edmonton, and Metro Vancouver.
IT/OT Network Segregation: Technical Insights
Straight answers for Plant Operations Directors, Logistics VPs, and Chief Information Security Officers.
In a flat or unsegmented network, an infection starting on a corporate workstation—such as an employee opening a malicious phishing attachment or downloading a rogue executable—can immediately traverse IP subnets into critical operational technology (OT). Because legacy industrial devices have zero local antivirus or endpoint protection, threat actors easily scan local subnets to compromise automated storage and retrieval systems (ASRS), programmable logic controllers (PLCs), ammonia refrigeration sensors, conveyor sorting loops, and barcode scanning servers. By segmenting IT and OT environments, QueryTel ensures that corporate cyber incidents cannot jump across the boundary to halt physical facility operations.
QueryTel follows a non-intrusive phased methodology. We begin in passive discovery mode using SPAN/mirror ports and Fortinet OT telemetry to catalog every connected PLC, HMI, WMS terminal, and sensor without injecting packets or interrupting real-time control loops. Once communication baselines are established, we construct an Industrial Demilitarized Zone (IDMZ / Level 3.5) utilizing Fortinet FortiGate NGFWs. Policies are initially deployed in monitor-only audit mode to verify zero legitimate traffic is dropped, before switching to active enforcement with Deep Packet Inspection for industrial protocols like Modbus TCP, EtherNet/IP, and PROFINET.
Standard IT firewalls only inspect basic layer 4 TCP/UDP ports, allowing any malicious payload traversing port 502 (Modbus) or 44818 (EtherNet/IP) to pass untouched. Fortinet FortiGate firewalls equipped with the FortiGuard Industrial Security Service perform Deep Packet Inspection (DPI) directly on operational protocols. They parse OT protocol commands down to the function code level. This allows QueryTel to enforce granular rules such as permitting read-only polling of refrigeration temperature sensors while cryptographically blocking unauthorized PLC firmware flashing or logic rewrite commands from unauthorized IP ranges.
QueryTel replaces unmanaged TeamViewer sessions, shared desktop logins, and persistent direct VPNs with Fortinet Zero-Trust Network Access (ZTNA) and hardened jump boxes located in the Industrial DMZ. External contractors authenticate via strict Multi-Factor Authentication (MFA), undergo device posture checks, and are granted least-privilege access restricted exclusively to the specific PLC or HMI IP address they maintain. All remote vendor sessions are encrypted, time-bounded, and recorded with full session logging for regulatory and forensic auditing.
Yes. Through our specialized hardware procurement division BrokerBand and our nationwide field dispatch smart hands network, QueryTel delivers a complete end-to-end turnkey solution. We source enterprise and ruggedized Fortinet FortiGate appliances, pre-stage and configure them in our Mississauga staging lab, ship them to sites across Ontario, Quebec, Alberta, and British Columbia, and deploy certified technicians to execute structured fiber/Cat6 cabling, rack mounting, cutovers, and on-site testing.
Schedule a confidential, non-intrusive IT/OT risk assessment with QueryTel's industrial cybersecurity engineers. We will inspect your current network topology, identify unmonitored vendor pathways, and architect a turnkey Fortinet FortiGate micro-segmentation blueprint with guaranteed zero downtime.
Corporate HQ: Exchange Tower, 130 King Street West, Suite 1900, Toronto, ON M5X 1E3 · Serving all Canadian Provinces