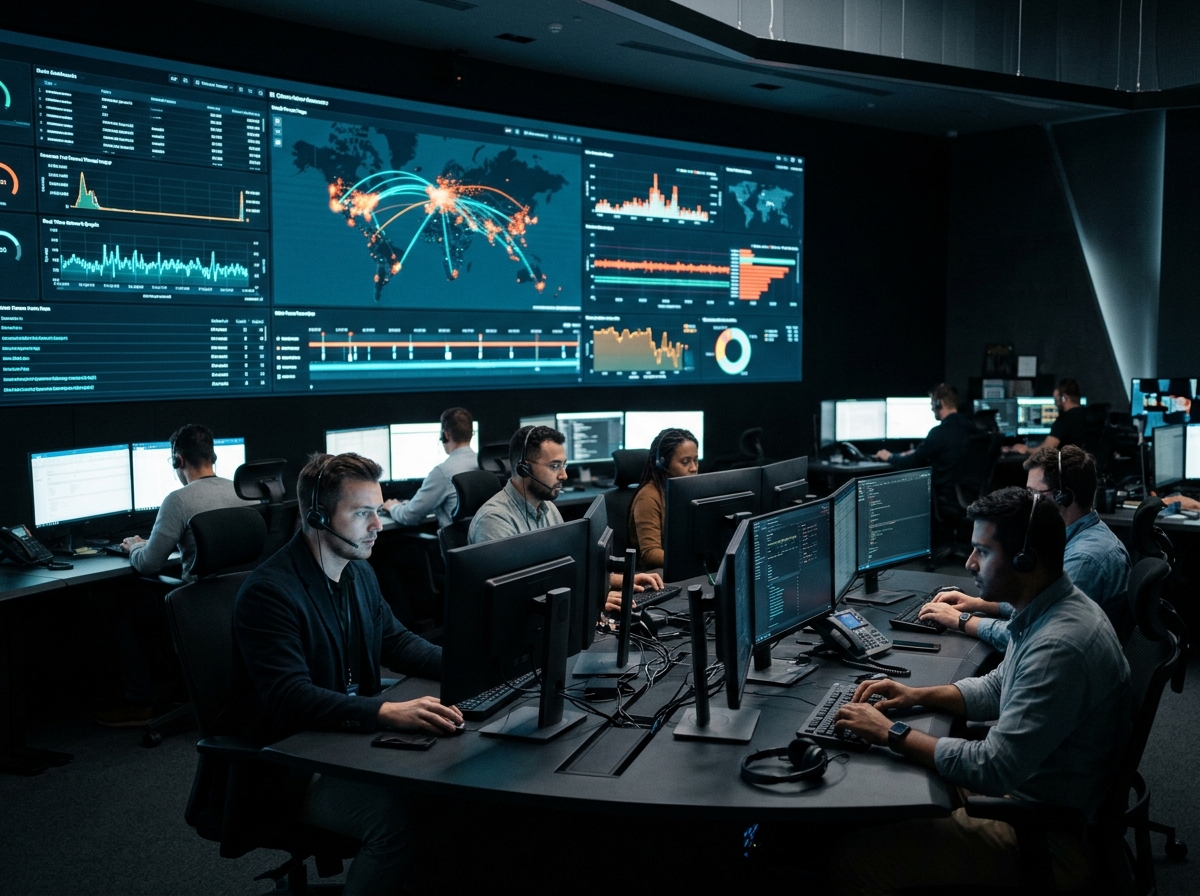
24/7 Cybersecurity Operations Center SOC Video Monitoring Wall
24/7 Canadian Sovereign SOC & MXDR

24/7 Managed SOC, MXDR & Canadian Cybersecurity Defense Against Modern Threats

Round-the-clock eyes-on-glass monitoring, AI-correlated SIEM detection, active threat hunting, and automated endpoint containment to stop ransomware and advanced social engineering in their tracks.

<15min
Incident Response SLA
24/7
Canadian Eyes-on-Glass
100%
Canadian Data Kept
24/7 Cybersecurity Operations Center SOC Video Monitoring Wall
Canadian Sovereign SOC
24/7/365 Eyes-on-Glass
Malwarebytes + Acronis
Automated Threat Quarantine
MTTD: <4 MIN | MEAN TIME TO RESPOND (MTTR): <15 MIN

Threat Landscape

Legacy Antivirus Is Dead. Here Is How Modern Cyber Attacks Infiltrate Businesses.

Threat actors no longer rely on noisy executable malware. They weaponize legitimate administrative tools, execute fileless scripts, establish encrypted reverse tunnels, and strike outside standard business hours.

Common Security Posture Failures

  • The "8am-5pm" Security Blind Spot: Over 82% of ransomware detonations occur on Friday nights or statutory holidays when internal IT staff are off-duty and cannot respond in time.
  • Reverse-Tunnel Exfiltration: Attackers deploy tools like Chisel, Ngrok, or outbound SSH tunnels that easily bypass legacy perimeter firewalls because they masquerade as normal HTTPS web traffic.
  • "ClickFix" / Fake CAPTCHA Droppers: Sophisticated phishing lures trick users into copying and pasting encoded PowerShell commands into their Run dialogue, executing memory-resident malware without tripping signature antivirus.
  • Uncorrelated Alert Fatigue: Disconnected security tools bombard administrators with thousands of daily notifications, causing true breach indicators to be completely overlooked.

The QueryTel 24/7 MXDR Solution

  • 24/7/365 Human-Led Triage: Certified Canadian security analysts monitor your telemetry continuously, actively isolating compromised machines within 15 minutes at 2:00 AM on Sunday.
  • Behavioral Anomaly & Tunnel Detection: Real-time heuristic monitoring catches unauthorized outbound tunneling protocols, anomalous network beacons, and unexpected parent-child script execution.
  • Script Execution Control & AMSI Defense: Antimalware Scan Interface (AMSI) hooks intercept memory-based PowerShell commands before execution, neutralizing social engineering droppers instantly.
  • Cross-Layer Telemetry Correlation: Our SIEM ingests firewall, Active Directory, cloud, endpoint, and email logs into a single pane of glass, distilling thousands of events into actionable incident alerts.

Enterprise Defense Ecosystem

Core Security Technologies, MXDR Architecture & Deliverables

We combine tier-1 enterprise detection agents with custom threat intelligence feeds, continuous vulnerability monitoring, and human security analysis.

24/7 Canadian-Soil SOC Monitoring

Continuous surveillance by Canadian security analysts operating out of Toronto and Montreal. We ingest telemetry from all corporate assets, filter false positives, and coordinate immediate containment.

  • • Sub-15 minute Mean Time to Respond (MTTR)
  • • Dedicated escalation engineer assigned to your account
  • • 100% Canadian data sovereignty & residency compliance

Managed XDR (Malwarebytes & Acronis)

Next-generation endpoint detection and response (EDR) powered by Malwarebytes for Business and Acronis Cyber Protect. Provides continuous process behavioral analysis, exploit mitigation, and automated ransomware rollback.

  • • Kernel-level behavioral threat detection
  • • Instant cryptographic endpoint network isolation
  • • Automated shadow-copy local volume rollback

SIEM Log Aggregation & Correlation

Centralized ingestion of event logs across Fortinet firewalls, Active Directory, Microsoft 365, VPN gateways, and cloud servers. Machine learning correlations spot multi-stage attack patterns that point solutions miss.

  • • 365-day encrypted log retention for compliance audits
  • • MITRE ATT&CK framework telemetry mapping
  • • User and Entity Behavior Analytics (UEBA)

Reverse-Tunnel & Exfiltration Defense

Identify and terminate unauthorized outbound tunnels (Chisel, Ligolo-ng, Ngrok, Cloudflare) used by modern cybercriminals to bypass NAT firewalls. Detects hidden C2 beacons and unauthorized data exfiltration attempts.

  • • Outbound TLS certificate inspection & entropy analysis
  • • Process execution tree auditing for script engines
  • • High-risk egress port filtering and strict DNS sinkholing

Advanced Email Threat Protection

Block business email compromise (BEC), VIP executive impersonation, and weaponized PDF/Office attachments before they reach inboxes. Includes DMARC/DKIM/SPF enforcement and cloud sandboxing.

  • • Real-time URL link rewriting and click-time inspection
  • • Zero-day attachment detonation sandbox
  • • Automated mailbox remediation and retroactive purge

Cyber Insurance Underwriting Compliance

Canadian insurance carriers routinely deny policies to businesses without 24/7 monitoring. QueryTel provides the exact attestations, log architecture, and controls required to pass cyber insurance renewals with zero friction.

  • • Official SOC 2 compliance documentation for brokers
  • • Monthly executive vulnerability risk scoring
  • • Incident response SLA documentation & tabletop runbooks

Security Operations Framework

How QueryTel Onboards & Protects Your Enterprise

A seamless 4-stage onboarding model that establishes active 24/7 SOC monitoring in under 7 business days with zero downtime.

01

Posture Audit & Threat Discovery

We scan your external attack surface, audit Active Directory hygiene, inspect firewall rulesets, and identify dormant vulnerabilities or unpatched shadow IT assets.

02

Agent Rollout & SIEM Ingestion

We deploy lightweight MXDR endpoint sensors via Group Policy or Intune, configure firewall syslog forwarding, and ingest cloud identity telemetry into our Canadian SIEM.

03

Baseline Tuning & Runbook Design

Our analysts spend 7 days baselining normal operational network traffic to eliminate false positives and establish customized incident response escalation workflows.

04

Active 24/7/365 Containment

Your environment transitions into continuous active monitoring. Threats are intercepted and neutralized in real time, backed by monthly executive threat reports.

Canadian Security Headquarters

Canadian Security Operations & National Incident Response Dispatch

QueryTel’s Security Operations Center is anchored at Exchange Tower, 130 King Street West, Suite 1900, Toronto, Ontario M5X 1E3, providing enterprise cyber defense across Canada’s commercial hubs.

In the event of an advanced persistent threat (APT) requiring physical forensics or emergency server room isolation, our mobile field engineering teams provide on-site dispatch across Mississauga, Brampton, Vaughan, Toronto, Oakville, and Hamilton, backed by regional offices across Canada:

Engineering Deployment Architecture

Field-Validated Infrastructure & Active Deployments

Cybersecurity Network Threat Stream
● Cybersecurity Network Threat Stream
Encrypted Datacenter Vault Infrastructure
● Encrypted Datacenter Vault Infrastructure

Security Operations FAQ

Managed SOC & Threat Defense FAQ

Straightforward answers to critical questions regarding 24/7 SOC SLAs, threat containment, and data sovereignty.

Most internal IT teams operate on a standard 8am–5pm schedule, leaving enterprises blind to attacks during nights, weekends, and holidays—the exact windows when over 82% of ransomware detonations occur. Building an internal 24/7/365 SOC requires a minimum of 8 to 12 certified security analysts, expensive SIEM licensing, and ongoing training, costing upwards of $750,000 annually. QueryTel provides immediate, turnkey access to a Canadian-based Security Operations Center staffed by Tier-2 and Tier-3 analysts who monitor, correlate, and actively isolate host threats in real time at a predictable monthly cost.
Modern threat actors increasingly bypass traditional perimeter firewalls by tricking employees into executing malicious PowerShell one-liners (known as 'ClickFix' or 'TerminalFix' fake CAPTCHA lures) or by installing legitimate developer tools (such as Chisel, Ngrok, or Cloudflare Tunnels) to establish outbound reverse tunnels. QueryTel's MXDR continuously inspects parent-child process executions (such as mshta.exe or powershell.exe spawned from browser processes), terminates unauthorized reverse-tunnel connections, and blocks unauthorized outbound SSH/TLS proxy channels before data exfiltration occurs.
Yes. 100% of our SIEM telemetry, packet logs, and incident forensic records are processed and stored exclusively in Tier-III and Tier-IV Canadian data center facilities located in Toronto and Montreal. This architecture guarantees full compliance with Canada's Personal Information Protection and Electronic Documents Act (PIPEDA), Quebec's Law 25, and Canadian public-sector data sovereignty requirements, shielding your corporate records from foreign legal overreach such as the US CLOUD Act.
QueryTel guarantees a sub-15 minute Mean Time to Respond (MTTR) for high-severity security incidents. Through our automated MXDR orchestration, infected endpoints are cryptographically isolated from the network within seconds of malicious activity detection, cutting off lateral attacker movement while preserving forensic memory state. Our human security analysts simultaneously contact your designated escalation leaders and initiate incident containment protocols.
Yes. Canadian insurance underwriters now strictly mandate 24/7 centralized log monitoring, Endpoint Detection and Response (EDR) with active human triage, multi-factor authentication (MFA) enforcement, and immutable off-site backups before issuing or renewing commercial cyber liability policies. QueryTel satisfies every mandatory underwriting requirement and provides formal SOC compliance attestations to assist your insurance carrier audit.
Zero-Risk Threat Assessment

Stop Relying on Luck. Protect Your Business Around the Clock.

Schedule your comprehensive security posture assessment with a QueryTel senior cybersecurity architect. We’ll audit your external attack surface, review endpoint controls, and deliver a transparent threat mitigation roadmap.

Fixed-price monthly SOC subscriptions with no long-term vendor lock-in. 100% Canadian data residency.