Microsoft Azure • Canada Central (Toronto) & East (Quebec)

Enterprise Azure Cloud, Microsoft Entra ID & Governed AI.

QueryTel architects sovereign Microsoft Azure environments, deploys Zero-Trust Entra ID Conditional Access & PIM, provisions Azure Virtual Desktop (AVD), and deploys Private Enterprise AI (Anthropic Claude & Azure OpenAI) governed by Microsoft Purview and protected 24/7 by QueryTel Sentinel Agentic SOC.

Zero-Trust
Entra ID & FIDO2 MFA
100%
Sovereign Data Residency
0% Leak
Private AI Model Boundary
Sub-Second
Sentinel SOC Threat Response
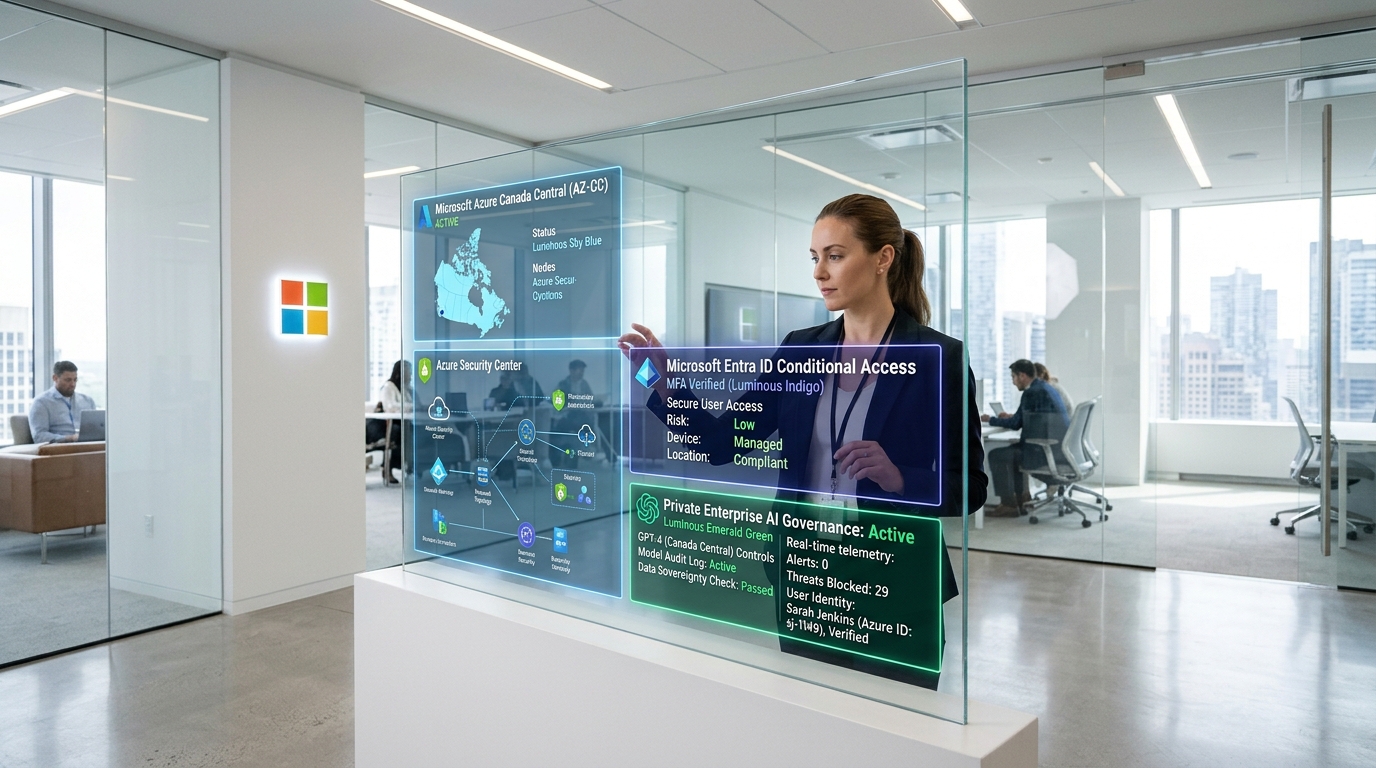
QueryTel Azure Cloud, Entra ID Zero-Trust & Governed AI Operations Studio
AZURE CANADA CENTRAL • ENTRA ID ZERO-TRUST ENFORCED

Governed Multi-Tenant Identity, AVD & Enterprise AI Architecture

Engineered Across Microsoft Cloud & AI:
Microsoft Entra ID P1/P2 Azure Landing Zones (CAF) Azure Virtual Desktop (AVD) Anthropic Claude on Azure / Bedrock Azure OpenAI Private VNet Microsoft Purview DLP Azure ExpressRoute Sentinel SOC + MXDR Linked
Why Modern Enterprises Choose QueryTel

Eliminate Identity Compromise, Uncontrolled AI Leakage & Cloud Sprawl

Legacy Active Directory syncs, unhardened Entra ID defaults, ungoverned public AI tools, and unmanaged Azure subscriptions expose enterprises to identity theft and regulatory fines. We engineer hardened, zero-trust cloud foundations.

Legacy & Default Cloud Vulnerabilities

Weak Passwords, Global Admin Sprawl & Shadow AI

  • Permanent Global Admin Assignments: 10+ IT accounts permanently assigned Global Administrator rights without Privileged Identity Management (PIM) or Just-In-Time elevation.
  • Phishable SMS / Push MFA: Employees falling prey to adversary-in-the-middle (AiTM) reverse-proxy phishing due to lack of FIDO2 passkeys and device-bound Conditional Access.
  • Uncontrolled Shadow AI & Data Exfiltration: Staff pasting proprietary customer IP, legal contracts, and financial records into consumer AI models without audit logging.
  • Disconnected Threat Telemetry: Impossible Travel logins and risky sign-ins go unnoticed because Azure logs are siloed away from 24/7 SOC containment.
QueryTel Zero-Trust Standard

Zero-Trust Entra ID, Governed AI & 24/7 Sentinel SOC

  • Conditional Access & FIDO2 Hardware Passkeys: Enforces device compliance (Microsoft Intune), compliant Canadian IP boundaries, and phishing-resistant FIDO2 authentication.
  • Privileged Identity Management (PIM): Zero standing privileges. Administrators must request time-bound elevation with manager approval, ticket rationale, and hardware MFA.
  • Private Enterprise AI (Claude & Azure OpenAI): Zero training-data leakage, private Azure VNet endpoints, and Microsoft Purview DLP guardrails protecting enterprise IP.
  • Closed-Loop Sentinel SOC & MXDR Correlation: Ingests Entra ID sign-in risks, token revocations, and Microsoft 365 audit logs into QueryTel Sentinel Agentic SOC in real time.
Enterprise Cloud & AI Engineering

Six Core Microsoft Azure, Entra ID & Enterprise AI Capabilities

Hover over each capability card below. Every Azure workload and Entra ID policy is codified in Bicep or Terraform, mapped to the Microsoft Cloud Adoption Framework (CAF), and backed by Canadian engineering support.

Pillar 01 • Identity Governance

Microsoft Entra ID Zero-Trust, Conditional Access & PIM

Eliminate passwords and unauthorized tenant access with Conditional Access, FIDO2 passkeys, Privileged Identity Management (PIM), and continuous session token evaluation against impossible travel and credential compromise.

Conditional Access Entra PIM (JIT) FIDO2 Passkeys
Pillar 02 • Sovereign Infrastructure

Canadian Azure Landing Zones (Canada Central & East)

Scalable enterprise landing zones codified in Bicep / Terraform according to the Microsoft Cloud Adoption Framework (CAF). Hard guardrails ensure data resides solely in Toronto (`Canada Central`) and Quebec City (`Canada East`).

Azure Policy CAF Hub-Spoke PIPEDA / Law 25
Pillar 03 • Governed AI

Private Enterprise AI: Anthropic Claude, Azure OpenAI & RAG

Deploy private LLM workloads—including Anthropic Claude and Azure OpenAI—inside customer-isolated Azure VNets with zero training-data leakage, vector search RAG pipelines, and Microsoft Purview DLP content boundaries.

Anthropic Claude Azure OpenAI Purview DLP
Pillar 04 • Modern Work

Azure Virtual Desktop (AVD) & Windows 365 Cloud PC

Deliver high-performance, secure Windows 11 multi-session virtual desktops to hybrid employees and contractors with FSLogix profile caching, GPU acceleration, and Entra ID Conditional Access device gating.

Azure Virtual Desktop FSLogix Profiles Windows 365
Pillar 05 • Hybrid Networking

Azure ExpressRoute, Virtual WAN & Fortinet NGFW

Connect headquarters, branch offices, and manufacturing plants directly to Azure with private ExpressRoute circuits, global Virtual WAN, and active-active Fortinet FortiGate-VM next-generation firewall inspection clusters.

ExpressRoute Azure Virtual WAN FortiGate-VM NGFW
Pillar 06 • SecOps & FinOps

Defender for Cloud, Sentinel Agentic SOC & Azure FinOps

Continuous posture management (CSPM), automated Azure Cost Management right-sizing, Reserved Instance planning, and live correlation of Entra ID sign-in risks into QueryTel Sentinel Agentic SOC.

Defender for Cloud Azure FinOps Sentinel SOC v5.0
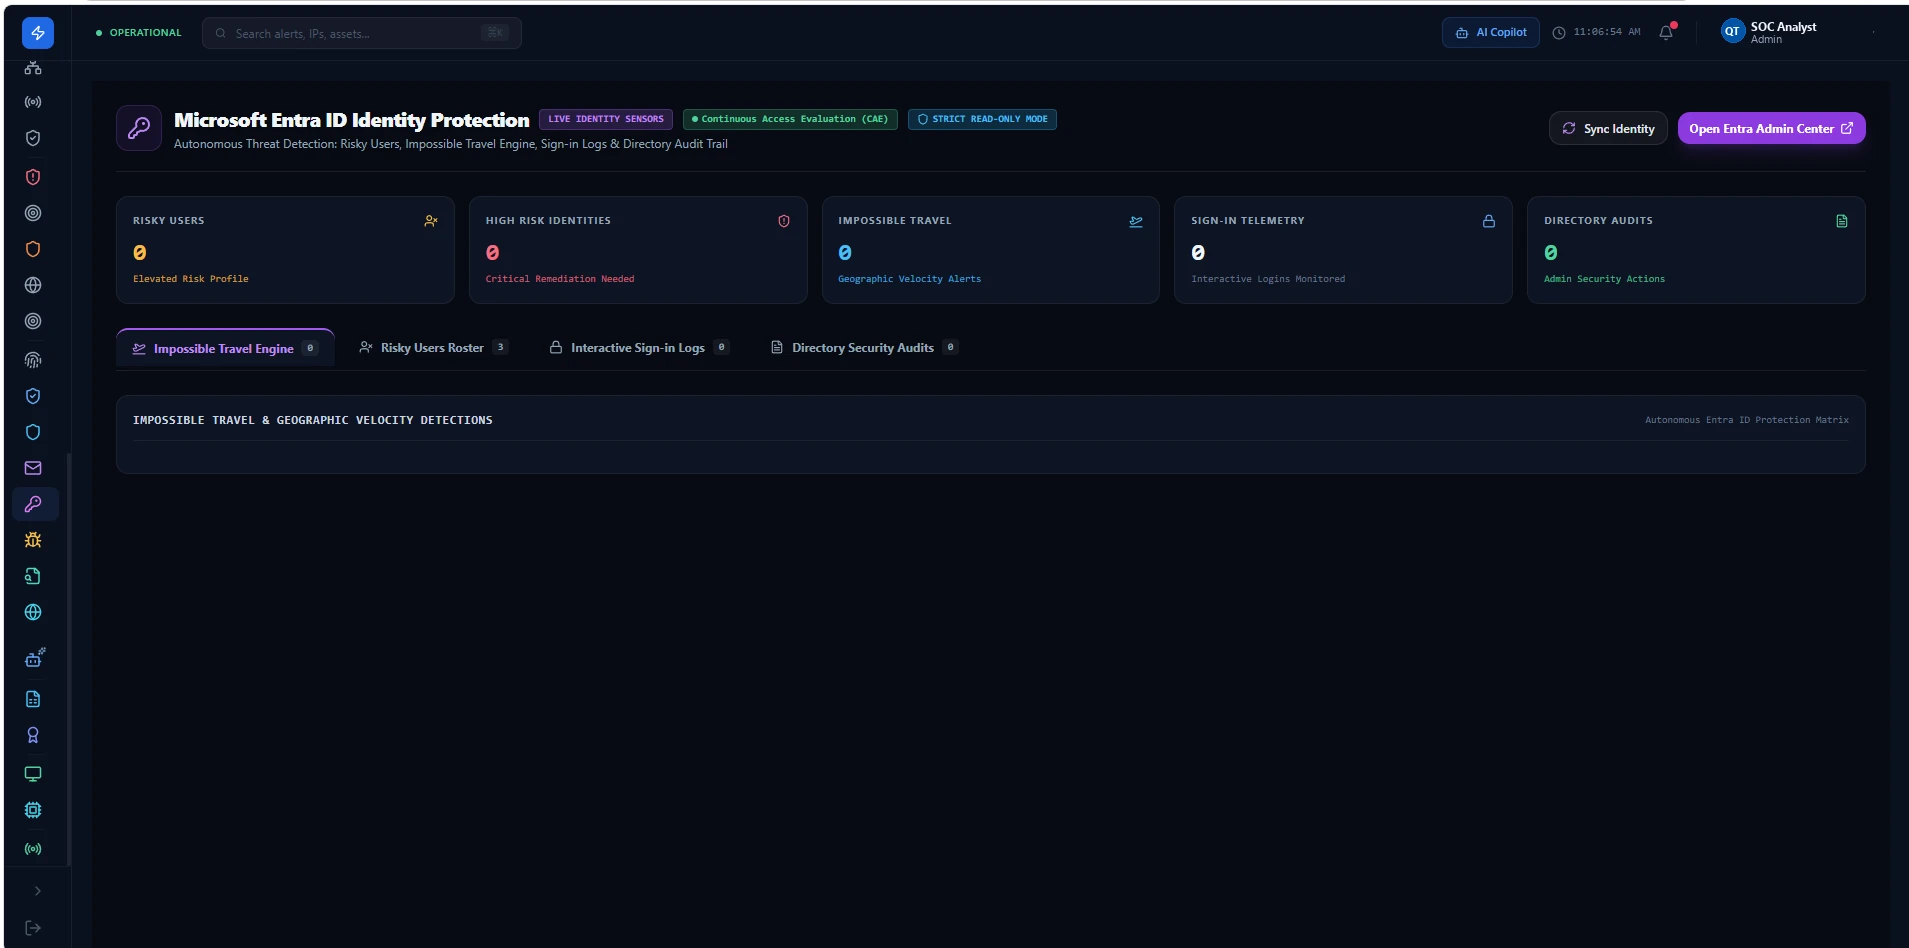
REAL SANITIZED ENTRA ID RISK TELEMETRY Sentinel SOC v5.0 Integrated
QueryTel Sentinel SOC & MXDR Live Microsoft Entra ID Identity Protection Telemetry
Real production Microsoft Entra ID tenant telemetry monitored by QueryTel: High/Medium user risk scoring, impossible travel detections, and automated session revocation.
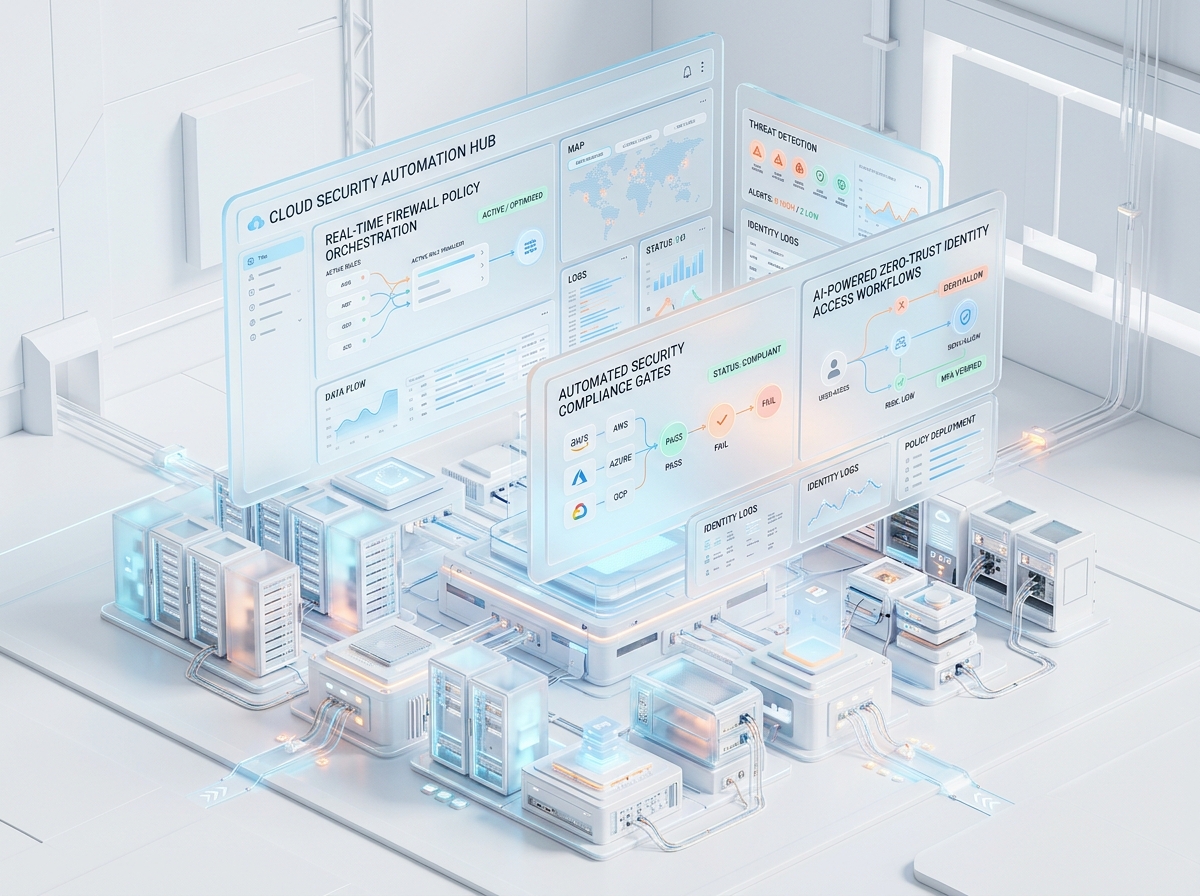
3D Glassmorphic Cloud Security Automation and Zero-Trust Identity Hub
Zero-Trust Identity Fabric
Automated Compliance Gates & MFA
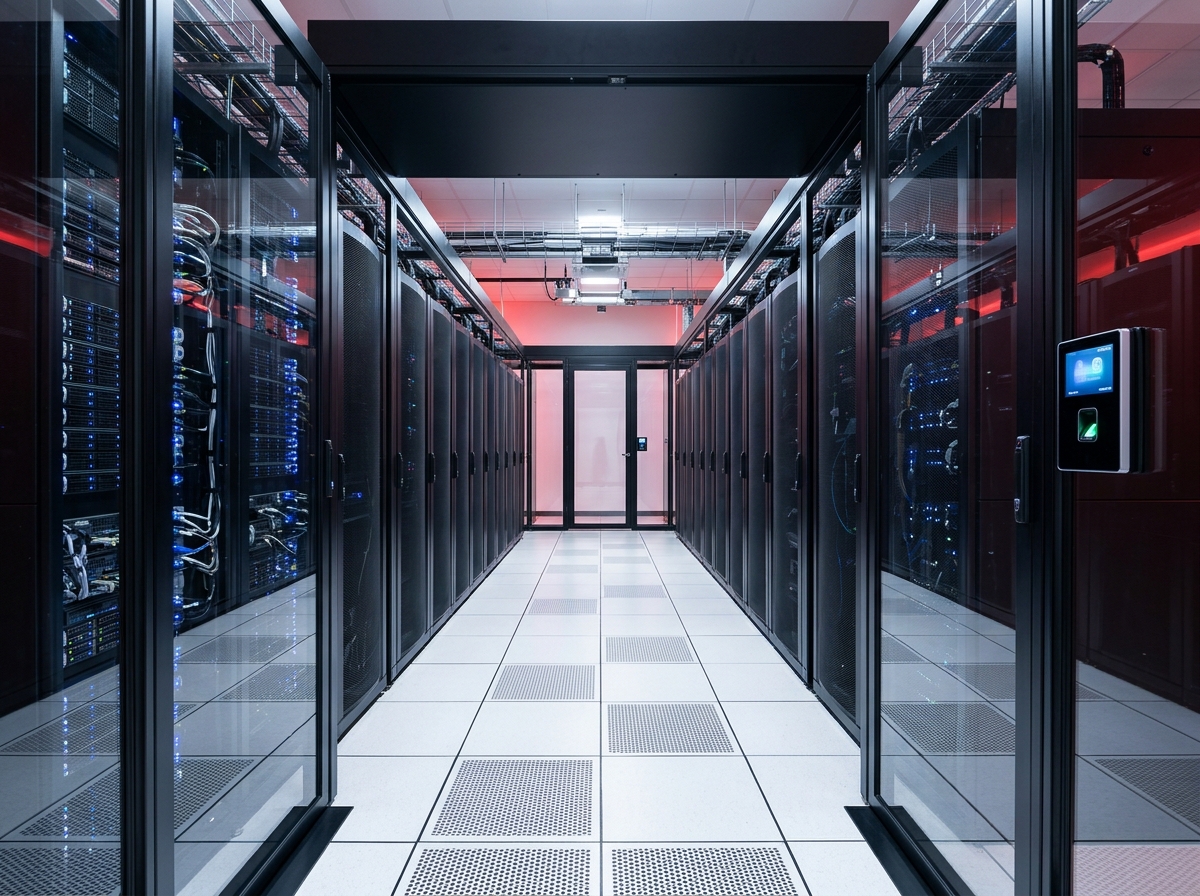
Sovereign Canadian Datacenter Operations with Biometric Access Control
Sovereign Canadian Core
Biometric & SOC 2 Type II Audited
Multi-Vendor Cloud Defense Fabric

How QueryTel Sentinel SOC & Email MXDR Protect Your Azure & Entra ID Tenants

Identity is the modern enterprise security perimeter. QueryTel natively binds your Microsoft 365 and Azure environments into our proprietary Sentinel Agentic SOC and QueryTel Email MXDR platforms.

01

Impossible Travel & Token Theft Correlation

Detects when an account signs in from Toronto and Amsterdam within minutes, immediately flagging adversary-in-the-middle (AiTM) session token hijacking.

02

Automated SOAR Revocation & Passwordless Reset

Sentinel executes automated or analyst-gated Microsoft Graph API actions to revoke all active refresh tokens, disable compromised user accounts, and enforce step-up FIDO2 verification.

03

Governed Enterprise AI DLP Telemetry

Monitors private Anthropic Claude and Azure OpenAI prompt activity through Microsoft Purview audit logs, detecting unauthorized attempts to prompt-inject or extract sensitive corporate records.

Microsoft Cloud Adoption Framework (CAF)

Structured Azure & Zero-Trust Modernization in Four Phases

From identity posture audit to scalable Canadian cloud operations and private enterprise AI deployment.

PHASE 01 • WEEKS 1–2

Identity & Tenant Audit

Comprehensive review of Entra ID Conditional Access policies, stale Global Admins, hybrid AD sync hygiene, and Azure subscription spend.

PHASE 02 • WEEKS 3–4

Landing Zones & PIM

Codify sovereign Bicep/Terraform Landing Zones in Canada Central/East, deploy Entra Privileged Identity Management, and roll out FIDO2 passkeys.

PHASE 03 • WEEKS 5–8

AVD & Governed AI

Migrate remote workloads to Azure Virtual Desktop, configure ExpressRoute / SD-WAN tunnels, and deploy private Claude / Azure OpenAI sandbox VNets.

PHASE 04 • ONGOING 24/7

Sentinel SOC & FinOps

24/7 Sentinel Agentic SOC monitoring, continuous Purview DLP audit logging, Reserved Instance optimization, and monthly executive security reviews.

Azure, Entra ID & AI FAQs

Frequently Asked Questions About QueryTel Azure & Entra ID Services

QueryTel architects Azure Landing Zones exclusively pinned to Azure Canada Central (Toronto) and Azure Canada East (Quebec City). Using Azure Policy definitions and management groups, we enforce hard geographical boundary restrictions so data at rest, in transit, and AI token workloads never leave sovereign Canadian borders—fully complying with PIPEDA, Quebec Law 25, and public-sector cloud frameworks.
Microsoft rebranded and expanded Azure Active Directory into Microsoft Entra ID, encompassing identity and network access products. Entra ID includes advanced capabilities such as continuous Conditional Access evaluation, Privileged Identity Management (PIM) with time-gated elevation, Entra Verified ID, FIDO2 passwordless passkeys, and real-time Identity Protection against credential stuffing and impossible travel.
QueryTel deploys enterprise AI models—including Anthropic Claude and Azure OpenAI—inside dedicated, customer-owned Azure virtual networks (VNets) with Private Endpoints. We enforce contractual and technical Zero Training Data guarantees (your corporate data is never used to train base foundation models), implement Retrieval-Augmented Generation (RAG) with vector databases, and integrate Microsoft Purview sensitivity labels to prevent confidential data leakage.
Our proprietary Sentinel Agentic SOC v5.0 platform integrates directly via Microsoft Graph API and Azure Monitor. Sentinel ingests Entra ID sign-in logs, audit events, risk events (such as Impossible Travel and leaked credentials), and Microsoft Defender for Cloud alerts. When high-severity identity compromise is detected, Sentinel can automatically revoke active user sessions, trigger an MFA reset, or quarantine an Azure VM in sub-seconds.
Yes. QueryTel executes seamless migrations using Azure Migrate and FSLogix profile containers. We transition on-premises Remote Desktop Services (RDS) or Citrix farms to Azure Virtual Desktop (AVD) multi-session Windows 11 environments, dramatically reducing licensing costs while giving your hybrid workforce secure access with Entra ID Conditional Access.
Yes. Many of our enterprise clients operate multi-cloud architectures. QueryTel unifies identity across clouds by federating Microsoft Entra ID with AWS IAM Identity Center, bridges networks with redundant ExpressRoute and Direct Connect through Fortinet SD-WAN, and correlates multi-cloud telemetry in QueryTel Sentinel Agentic SOC.
Schedule Your Azure & Entra ID Zero-Trust Review

Ready to Harden Microsoft Identity & Modernize on Azure?

Consult with QueryTel's Microsoft-certified Cloud Architects and Cybersecurity Engineers. We will inspect your Entra ID tenant security score, Conditional Access rules, Canadian data residency, and enterprise AI readiness.